Linux Server Hardening Basics
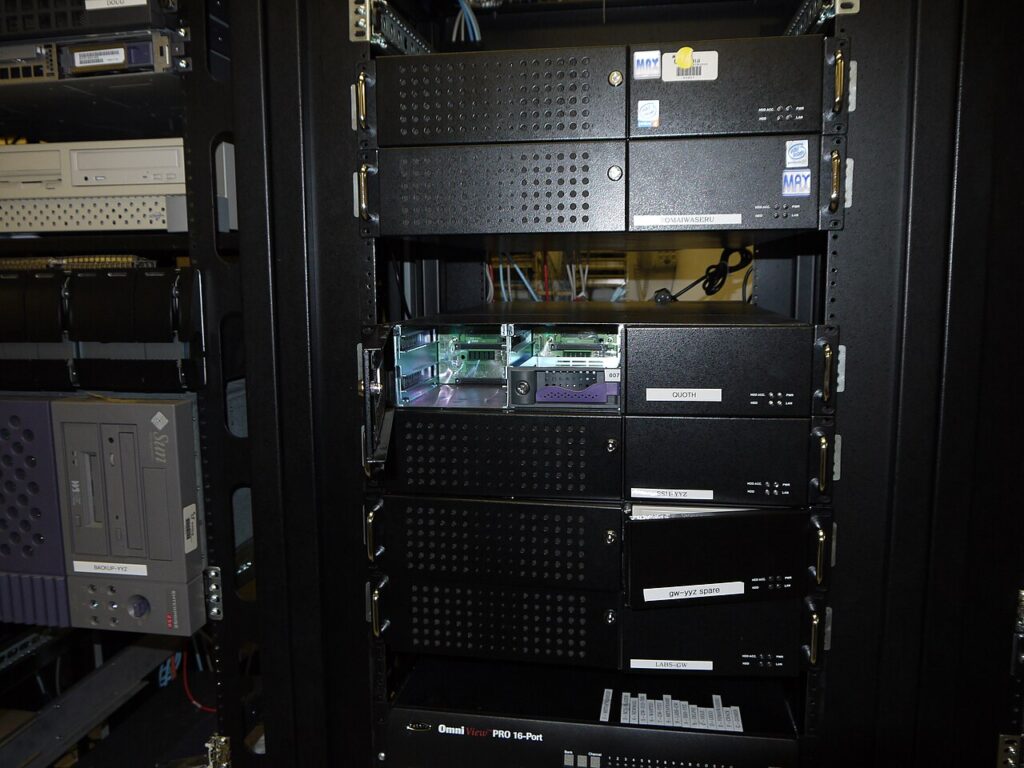
A fresh Linux server is not secure by default. Linux server hardening reduces the attack surface and makes compromise harder.
Update and minimize
Apply updates promptly, enable automatic security patches, and remove software and services you do not need. Fewer packages mean fewer vulnerabilities.
Secure access
Use SSH keys instead of passwords, disable root login, limit allowed users, and consider changing exposure with a VPN or allowlist. Add multi-factor authentication for administrators.
Firewall and network
Enable a host firewall that allows only required ports, and use tools such as fail2ban to block repeated login attempts.
Permissions and logging
Use least privilege with sudo, set proper file permissions, and enable auditing and centralized logs. Monitor for unexpected changes.
Backups and baselines
Take regular backups, test restores, and follow benchmarks such as CIS to keep configuration consistent.
Key takeaways
- Update and minimize: Apply updates promptly, enable automatic security patches, and remove software and services you do not need. Fewer packages mean fewer vulnerabilities.
- Secure access: Use SSH keys instead of passwords, disable root login, limit allowed users, and consider changing exposure with a VPN or allowlist. Add multi-factor authentication for administrators.
- Firewall and network: Enable a host firewall that allows only required ports, and use tools such as fail2ban to block repeated login attempts.
- Permissions and logging: Use least privilege with sudo, set proper file permissions, and enable auditing and centralized logs. Monitor for unexpected changes.
- Backups and baselines: Take regular backups, test restores, and follow benchmarks such as CIS to keep configuration consistent.
Putting it into practice
To apply this in your own organization, begin with a short assessment of where you stand on Linux server hardening today. Write down who owns it, which tools are involved, and the single biggest gap. Fix the highest-risk gap first, assign a clear date, and review progress after thirty days. Share what you learn with the team so improvements stick, and document the decisions you make so new staff can follow them. Revisit the topic every quarter, because threats, tools, and business needs change quickly, and small regular adjustments are far easier than large emergency fixes.
Common mistakes to avoid
Many teams struggle with Linux server hardening because they try to do everything at once, skip documentation, or treat it as a one-time project. Others rely on a single person who holds all the knowledge, or buy tools before defining the problem they need to solve. Avoid these traps by starting small, writing down simple procedures, spreading responsibility across the team, and checking results on a regular schedule. If something is not working, adjust quickly instead of abandoning the effort, and keep a short log of what you changed and why. That record makes future decisions faster and helps new colleagues understand the reasoning behind your approach.
Frequently asked questions
Do I need antivirus on Linux?
Often endpoint monitoring is still useful for servers.
How often should I patch?
Apply security updates as soon as practical.
Final thoughts
Update, minimize, lock down access, and monitor. Those basics stop most attacks on Linux servers.
Keep reading
- Endpoint Security
Forrester’s Three-Pillar Model for API Enablement Explained
- Endpoint Security
What to Do When a Company Phone Is Lost
- Endpoint Security
What Is TLS Inspection and Is It Safe?
- Endpoint Security
AI Will Change Most IT Jobs: How to Prepare